


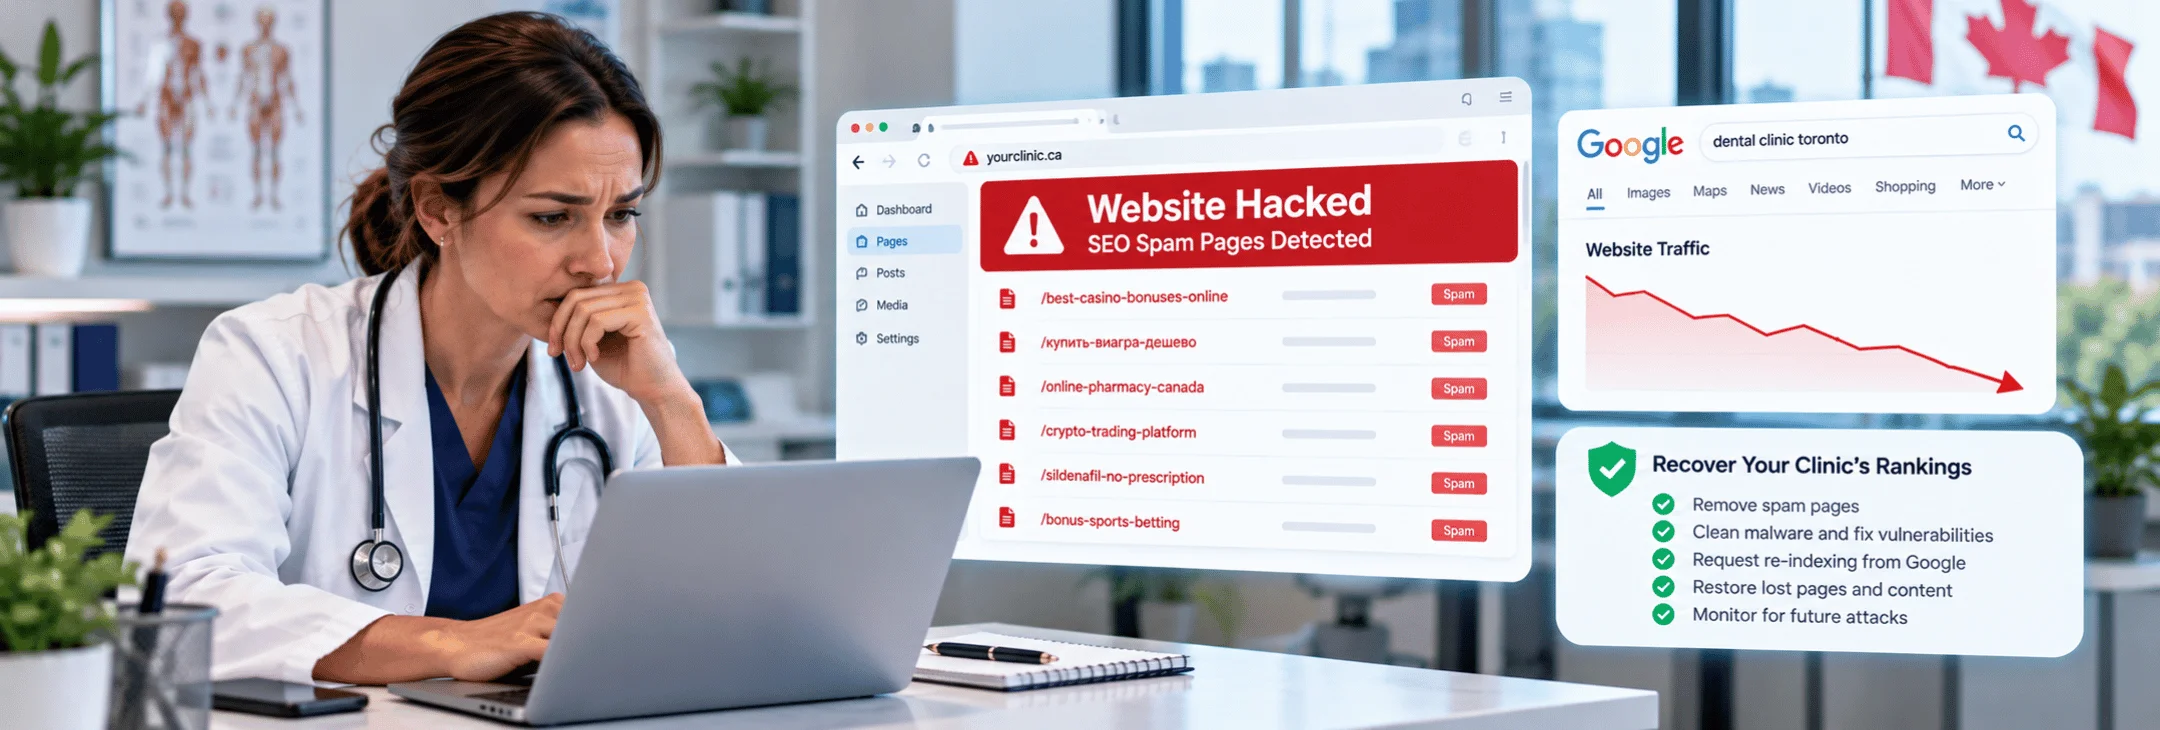
A strange search result can ruin a clinic owner's morning. Your homepage looks normal, yet Google shows pages about casinos, replica watches or pills under your domain. That pattern usually points to a website hacked with SEO spam, and it can hurt patient confidence fast. This guide walks Canadian practices through confirming the attack, cleaning it up, meeting privacy duties and blocking the next attempt.
Quick Answer for a Website Hacked With SEO Spam
Recovery follows a fixed order, and skipping ahead usually brings the spam back. The owner confirms the attack inside Search Console and takes a full backup of the files and the database. The web team then clears out the spam pages and closes the entry point the attacker used. Google reviews the site once the owner submits a request. A clinic that may have exposed patient records also checks its breach duties under PIPEDA or provincial law.
Warning Signs of a Hacked Clinic Website
A website hacked with SEO spam can look perfectly normal to the person who owns it. The damage usually hides in search results, in old URLs and in folders that staff never open. Clinic owners usually notice one of these signs first.
- Strange titles appear when you search your own domain, often in Japanese, Turkish or gambling languages.
- Odd URLs show up in the Pages report with random folder names and long strings of numbers.
- A warning label that reads "This site may be hacked" sits under your listing in Google.
- Patients report malicious redirects to casino or pharmacy pages after they click your listing.
- Search Console sends an email about a new owner that nobody at the clinic added.
The Security Issues report in Search Console gives the most reliable answer, because it lists the problems Google itself detected. Some infected pages still look fine when you open them. That trick is cloaking, and it shows Google one version of a page while you see another. Google's URL Inspection tool reveals what its crawler actually receives, so it often exposes spam that a normal browser misses.
Common Hacks That Target Healthcare Websites in Canada
Clinic sites make attractive targets for a simple reason. They carry local authority, steady traffic and clean link profiles that spammers want to borrow. Spammers know that spam pages on a trusted local domain rank faster than pages on a brand new site.
Most attacks enter through outdated plugins, weak passwords or an unpatched theme. The motive behind a website hacked with SEO spam is usually money, not patient records. Attackers want your search rankings working for their products.
The Japanese keyword hack deserves extra attention because the attacker often adds a new verified owner in Search Console. That owner can then submit a fake sitemap and push junk URLs into the index faster. Your team needs to remove any unfamiliar owner along with the verification file or rewrite rule behind it.
Also Read: Why Healthcare Websites Lose Rankings After Google Updates and How to Fix It
How to Clean Up a Website Hacked With SEO Spam and Request a Google Review
The cleanup for a website hacked with SEO spam works best as a sequence. Your team needs a full backup of the infected site before anyone deletes a file. That copy acts as evidence and as a safety net if the cleanup breaks something.
Find the Entry Point
Every hacked site recovery starts with one question. The attacker got in somehow, and that gap must close before anything else.
Step 1. Check Users and Owners
Your developer reviews every admin account on the site and every verified owner in Search Console. Every remaining admin account gets two-factor authentication before the site goes back online.
Step 2. Compare Files Against Clean Copies
Fresh copies of the CMS core, theme and plugins replace the existing ones. Files that changed around the date of the attack, or files with unusual sizes, often point straight to the backdoor.
Step 3. Inspect the .htaccess File and Hidden Scripts
The .htaccess file deserves a line-by-line check, since hackers love it for redirects and fake verification tokens. Some scripts check the visitor type and serve spam only to Google, which is classic cloaking. The usual culprits on clinic sites are outdated plugins and abandoned themes.
Remove Spam URLs
SEO spam removal covers both the files on your server and the pages already sitting in Google's index.
Step 1. Delete Injected Pages and Database Entries
Your team deletes every injected page, post and database record. Those URLs should return a 404 or 410 status code, which tells Google the content no longer exists.
Step 2. Clean the Sitemap and Robots File
Hackers often add a second sitemap or slip spam links into the real one. The clean sitemap lists only genuine clinic pages, and your team resubmits it in Search Console.
Step 3. Use the Removals Tool for Urgent Cases
Google's Removals tool hides a URL from search results for about six months. It works well for embarrassing spam pages that patients keep finding while the permanent 404 takes effect. Your staff should be caring for patients, not chasing spam.
Request Review
Google keeps its warning in place until it confirms the site is clean. A careful reconsideration request shortens that wait and lowers the chance of a rejection.
Step 1. Confirm the Site Is Clean
The Security Issues report lists sample URLs, not every infected page. Your team checks those samples with the URL Inspection tool, since cloaking can hide spam from a normal browser.
Step 2. Explain What You Changed
A strong request explains what the hack did, what your team removed and how it closed the gap.
Step 3. Wait for the Decision
Google sends an email when it receives the request and another when the review ends. Reviews for spam hacks can take several weeks because they sometimes involve manual checks. Your search rankings usually return gradually once Google trusts the site again.
Also Read: Medical Website SEO Audit Checklist 2026 and the Issues to Fix to Rank Higher
PIPEDA Breach Reporting and Provincial Duties for Canadian Clinics
A website hacked with SEO spam is a search problem first, but it can turn into a privacy problem quickly. A backdoor gives the attacker server access, and that access may reach booking forms, intake data or contact records. Online booking forms that store personal health information on the web server raise the stakes considerably.
PIPEDA applies to private sector organizations that handle personal information in commercial activity. It requires a report to the Privacy Commissioner when a breach creates a real risk of significant harm. The same test triggers direct notice to affected patients, and the law expects that notice as soon as feasible.
The risk test weighs how sensitive the data is and how likely someone is to misuse it. Personal health information almost always sits at the sensitive end of that scale. Quick, honest notice protects patient trust far better than silence.
Record keeping matters even when the clinic does not need to file a report. Every organization under PIPEDA keeps a record of each breach for two years, including the reasons it decided not to report.
The Privacy Commissioner also offers an online tool that walks organizations through the real risk of significant harm test. The federal PIPEDA breach reporting form asks for the cause, the date, the information involved and the number of people affected.
Provincial health privacy laws can apply instead of PIPEDA or alongside it.
- Ontario clinics that act as health information custodians under PHIPA notify affected patients at the first reasonable opportunity. They also report certain breaches to the provincial commissioner and send yearly breach statistics to that office.
- Alberta custodians under the Health Information Act notify the provincial commissioner, the Minister of Health and affected patients when a breach creates a risk of harm.
- Quebec and several other provinces have their own private sector or health privacy statutes with separate rules.
A privacy lawyer or your regulatory college can confirm which law covers your clinic.
Healthcare Website Security Habits That Prevent the Next Attack
Prevention costs far less than another cleanup. A hacked clinic website loses bookings every day it stays live. Clinics that adopt the habits below rarely see a website hacked with SEO spam a second time.
- Updates for the CMS, theme and plugins go in every week, and unused plugins come off the site completely.
- Unique passwords replace shared logins, so each staff member and vendor has separate access.
- Your hosting provider account needs two-factor authentication too, since a stolen hosting login bypasses every plugin setting.
- A full backup runs automatically every day and sits off the server, with a restore test every few months.
- Online forms send personal health information to a secure system rather than storing it inside the website database.
Healthcare website security also depends on who can touch the site. Old agency logins and former staff accounts are common gaps. The clinics we audit most often fall to outdated plugins that nobody has touched in a year. Your domain registrar login deserves two-factor authentication as well.
Patient trust recovers faster when the site looks and runs like a professional clinic again. Good healthcare website development builds security into the theme, hosting and forms from the start, rather than adding it later. A hacked clinic website should not decide what patients think of your care.
Final Thoughts on a Website Hacked With SEO Spam
A website hacked with SEO spam feels personal because your clinic name sits on every one of those junk URLs. The path back is clear, and most clinics regain their visibility. Every hacked site recovery rewards patience and the right order of work.
At Rankingeek, we help healthcare practices protect their online presence, recover lost search visibility, and build websites that patients can trust. Our team combines healthcare SEO, technical website optimisation, and secure website development to identify vulnerabilities, resolve ranking issues, and prevent future attacks.
If your clinic is dealing with SEO spam, suspicious redirects, or an unexplained drop in Google rankings, we can help you get your website back on track and restore patient confidence.
FAQs About Recovering From SEO Spam Hacks
Will my rankings come back after a hack?
Your search rankings usually return once Google confirms the site is clean. The climb is gradual, and key pages can take several weeks to regain their old positions as the spam pages drop out of the index.
How long does Google take to remove hacked pages?
Pages that return a 404 or 410 status fall out of the index over the following weeks as Google recrawls them. The Removals tool hides urgent URLs sooner, and a reconsideration request for spam hacks can take several weeks on its own.
Do I have to report a website hack to the Privacy Commissioner?
You only have to report it when the breach involves personal information and creates a real risk of significant harm. A pure spam injection may not meet that test, but you still record the incident and your reasoning. Ontario, Alberta and other provinces add their own health sector rules.
Can a website hacked with SEO spam harm patients' devices?
It can, especially when the attacker adds malicious redirects or download prompts. Google may then show a browser warning that scares off new bookings.
Should I clean the site or rebuild it?
A cleanup usually works when the entry point is clear, and the site is fairly recent. A rebuild makes more sense for old themes or sites that hackers keep breaking into, since a fresh build removes every hidden backdoor at once.